






Data Governance Frameworks for Indian BFSI 2026
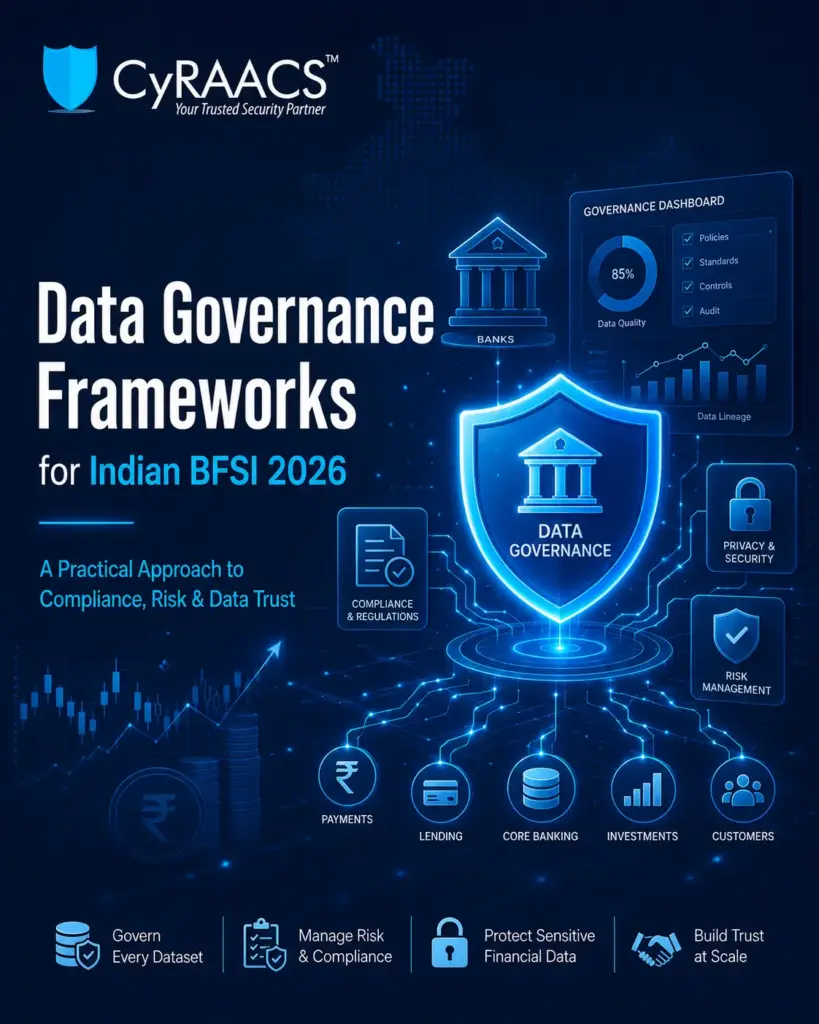
A data governance framework is the set of policies, roles, processes, and controls that an organisation uses to manage its data as a governed asset
Navigating SEBI’s New Cyber Resilience Guidelines: How CyRAACS Can Empower Your Cybersecurity Strategy
The Securities and Exchange Board of India (SEBI) has introduced new Cyber Resilience and Security Guidelines, setting a higher benchmark for financial institutions. As cyber threats evolve, regulatory bodies worldwide are tightening security measures to safeguard critical financial data and protect investors. These new SEBI guidelines emphasize risk management, incident response, and regulatory compliance, requiring organizations to adopt a proactive cybersecurity strategy.
Under Siege? Here is What to Do When You’re Hit by a DDoS Attack
While digital operations are crucial to business success, Distributed Denial of Service (DDoS) attacks have emerged as a prominent threat, targeting organizations of all sizes. These malicious attacks overwhelm a network, rendering websites and services unusable and inflicting significant damage to both operational capabilities and brand reputation. Understanding how to respond effectively to a DDoS […]
Embracing RBI’s Directive: A Guide to Strengthen Third-Party Risk Management
In today’s interconnected financial landscape, the reliance on third-party vendors has become increasingly prevalent, bringing both opportunities and risks. The Reserve Bank of India (RBI) has recognized the importance of robust Third-Party Risk Management (TPRM) systems to ensure the security and stability of financial institutions. Embracing the RBI’s directive on TPRM is not merely about […]
PHI vs. PII: Understanding the Differences and Their Impact on Data Privacy

In the realm of data privacy, terms like PHI (Protected Health Information) and PII (Personally Identifiable Information) are more than just buzzwords-they’re pivotal concepts in safeguarding individual privacy. While they might seem similar at a glance, they occupy distinct spaces in data protection, and understanding the distinctions between Protected Health Information (PHI) and Personally Identifiable […]
AI-Powered Phishing: The Next Big Cybersecurity Challenge
Phishing attacks have always been the pesky thorn in the side of cybersecurity, but with the advent of Artificial Intelligence (AI), these attacks have leveled up in a way that’s both impressive and alarming. Gone are the days of generic mass emails riddled with typos. Now, we’re facing hyper-personalized, slick, and adaptive phishing attempts that are harder to spot than ever before.
Top Cybersecurity Trends to Watch in 2025
Machine Learning (ML): Transforming Security Through Advanced Insights Machine Learning (ML), a branch of Artificial Intelligence (AI), empowers computers to analyze data, identify patterns, and improve performance without explicit programming. This adaptive learning enables systems to mimic human-like learning through experience gained from data. Key Applications of ML in Security By continuously learning and adapting […]
Control Driven GRC Solutions: Streamlining Risk Management and Compliance

In today’s complex regulatory landscape, effectively managing Governance, Risk, and Compliance (GRC) is paramount. Traditional approaches often prove cumbersome and inefficient, leaving organizations vulnerable to risks and non-compliance. A control-driven GRC product offers a powerful solution, streamlining GRC activities through automation and a centralized platform. This innovative approach empowers organizations to proactively manage risks, ensure […]
Leveraging GRC for Organizational Success: A Comprehensive Approach
Governance, Risk, and Compliance (GRC) plays a pivotal role in organizational success by providing a structured and integrated approach to managing an organization’s overall performance, addressing risks, and adhering to regulatory requirements. An effective GRC approach not only ensures that organizations operate ethically and responsibly but also supports their overall success by enhancing decision-making, managing […]
Cracking the Code: A Guide to Understanding and Complying with Regulatory Requirements
Compliance with government laws, regulations, and rules is essential for all organizations. A regulatory requirement is a directive imposed by a government entity on an organization. Numerous federal and state laws apply universally to organizations, dictating how they conduct their operations, manage employees, and engage with customers, among other aspects. Ensuring regulatory compliance is vital […]