CyRAACS SERVICE
Consulting services can provide the expertise and guidance needed to ensure your business is protected from malicious actors. Whether you’re looking to implement a comprehensive security strategy or simply need advice on compliance and data protection, a cybersecurity consultant can provide the support you need.

At CyRAACS, we perform an extensive Risk Assessment to identify the inherent and residual information security risks across the organization. Based on the assessment conducted, we recommend Risk Mitigation measures to ensure the appropriate security controls are in place in line with the organization risk appetite.

Business Continuity planning is essentially a form of insurance. It gives organizations the comfort of knowing that, even if disaster strikes, the damage won’t be overwhelming.
Having an effective Business Continuity Management ensures that organizations can continue to provide an acceptable service in the event of a disaster, helping them preserve their reputation and keep revenue coming in. In the event that its key management resources are compromised, it is critical for an organization to be proactive and create a viable plan of countermeasures.
CyRAACS’s business continuity professionals provide consultancy help in identifying risks arising from third party vendor networks, managing them effectively, and planning how you can operate, improving your organizational resilience.

An Information Security Maturity Model provides a path forward and enables the organization to periodically assess where it is along that path. Our unique qualitative and quantitative assessment model is adapted from the CMMI rating scale. CyRAACS’s Maturity Model Assessment framework helps to understand the organization’s risk exposure, and the maturity of the current information security program and identify areas for improvement, we also create benchmarks against other organizations and validate that security investments have improved security posture. We also provide a roadmap with opportunities in the areas of technology, process, and capabilities for information security.

For today’s way of the data treatment, it is an easy target to expose as organizations across the world are looking at the increasing amounts of data to deal with every day, this could be through e-mails, files, transactions, etc. Hence organizations urgently need to understand what their sensitive data is and where they are so that they can deploy appropriate controls to protect it. Data Flow Analysis (DFA) is the first step toward identifying sensitive data and implementing appropriate security controls for data protection.
CyRAACS’s DFA framework covers all the stages of the data lifecycle right from data acquisition to retirement. It helps to capture an accurate picture of the data flow at various stages within the organization. The output from DFA can act as key inputs to a Digital Rights Management (DRM) or Data Leakage Prevention (DLP) tool implementation, should an organization wish to implement those tools.

Build your future with us.
VAPT services that go beyond scanning to test real-world exploitability across applications, APIs, infrastructure, and cloud.
Choose the VAPT Approach That Fits Your Security Needs
Whether you need a point-in-time assessment or continuous visibility into your evolving attack surface, CyRAACS offers VAPT services designed to identify, validate, and prioritize real security risks.
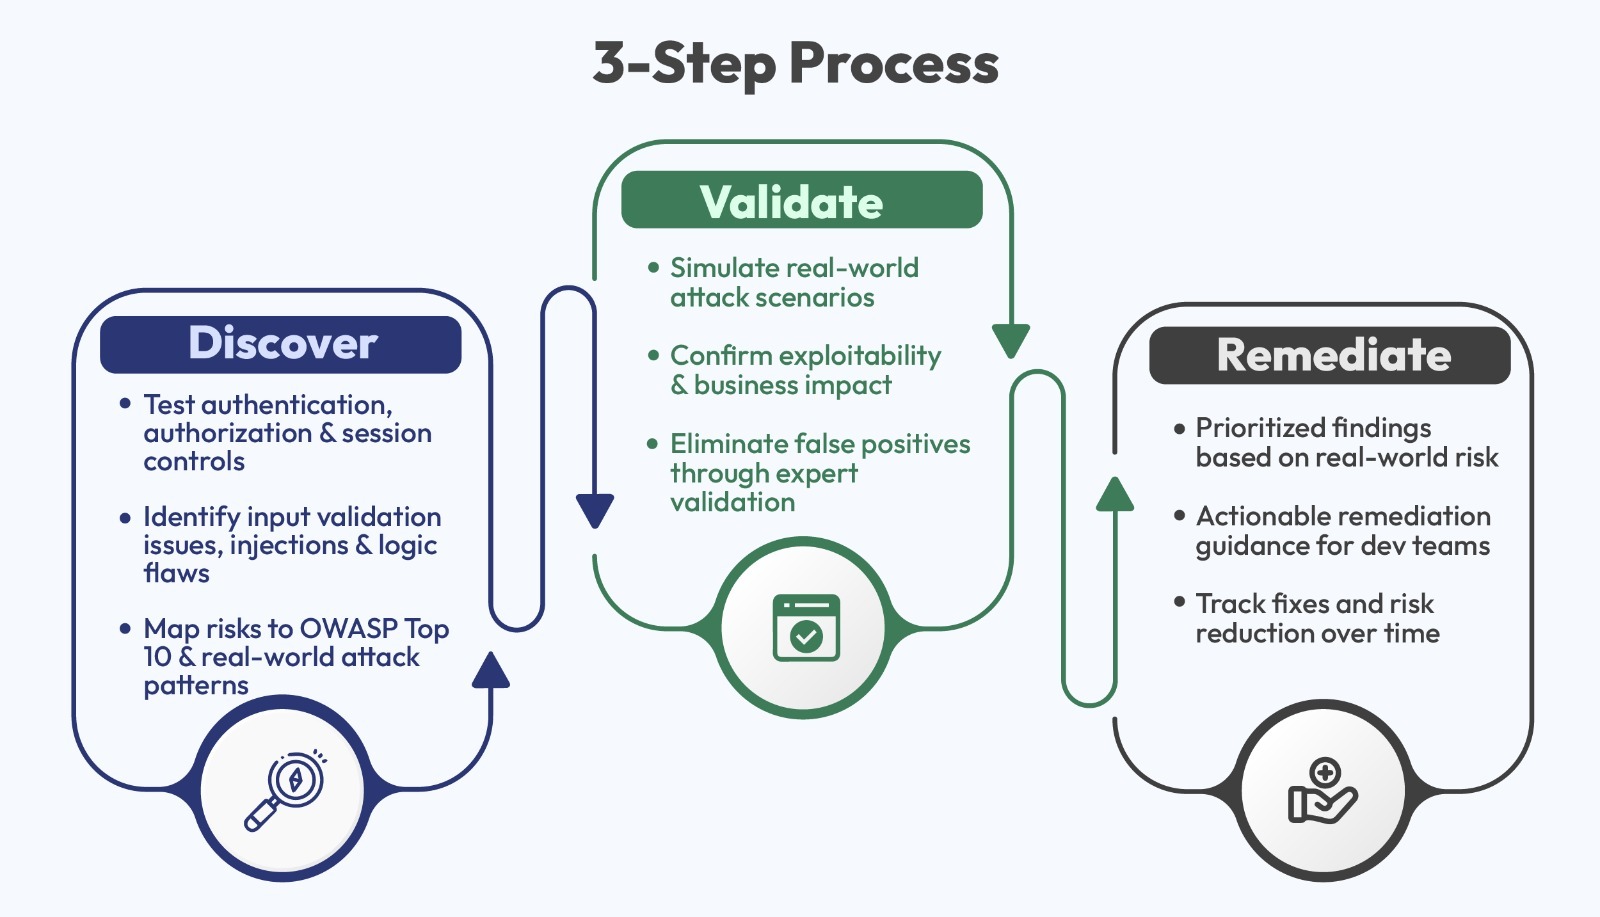
Our one-time VAPT engagements provide a comprehensive assessment of your applications, APIs, infrastructure, and cloud environments. We combine automated testing with expert-led manual validation to identify vulnerabilities, verify real-world exploitability, and provide prioritized remediation guidance.
Our Managed VAPT service goes beyond periodic testing with continuous assessment, expert validation, risk-based prioritization, and centralized remediation tracking. It helps organizations keep pace with changing applications, APIs, infrastructure, and cloud environments while continuously reducing security risk.
Our VAPT Testing Coverage Areas
API Security Testing
CyRAACS performs focused API security testing to identify vulnerabilities that can lead to data exposure, unauthorized access, and abuse of business logic. Our testing goes beyond specification checks to validate how APIs behave under real attack conditions.
⦁ Review API authentication, authorization, and access controls
⦁ Test for data exposure, input validation issues, and logic flaws
⦁ Identify API-specific risks aligned to OWASP API Security Top 10
⦁ Validate exploitability and potential impact on applications and backend systems
⦁ Provide prioritized remediation guidance for secure API design and deployment
Web Application Security Testing
Our web application penetration testing service identifies vulnerabilities that lead to unauthorized access, data exposure, and business logic abuse. We test how applications hold up under real attacker behavior, not just against a scanner’s checklist.
⦁ Test authentication, authorization, and session management controls
⦁ Identify input validation issues, injection flaws, and logic vulnerabilities
⦁ Assess risks aligned with OWASP Top 10 and real-world attack patterns
⦁ Validate exploitability and potential business impact
⦁ Provide prioritized remediation guidance for secure application development
Mobile Application Security Testing
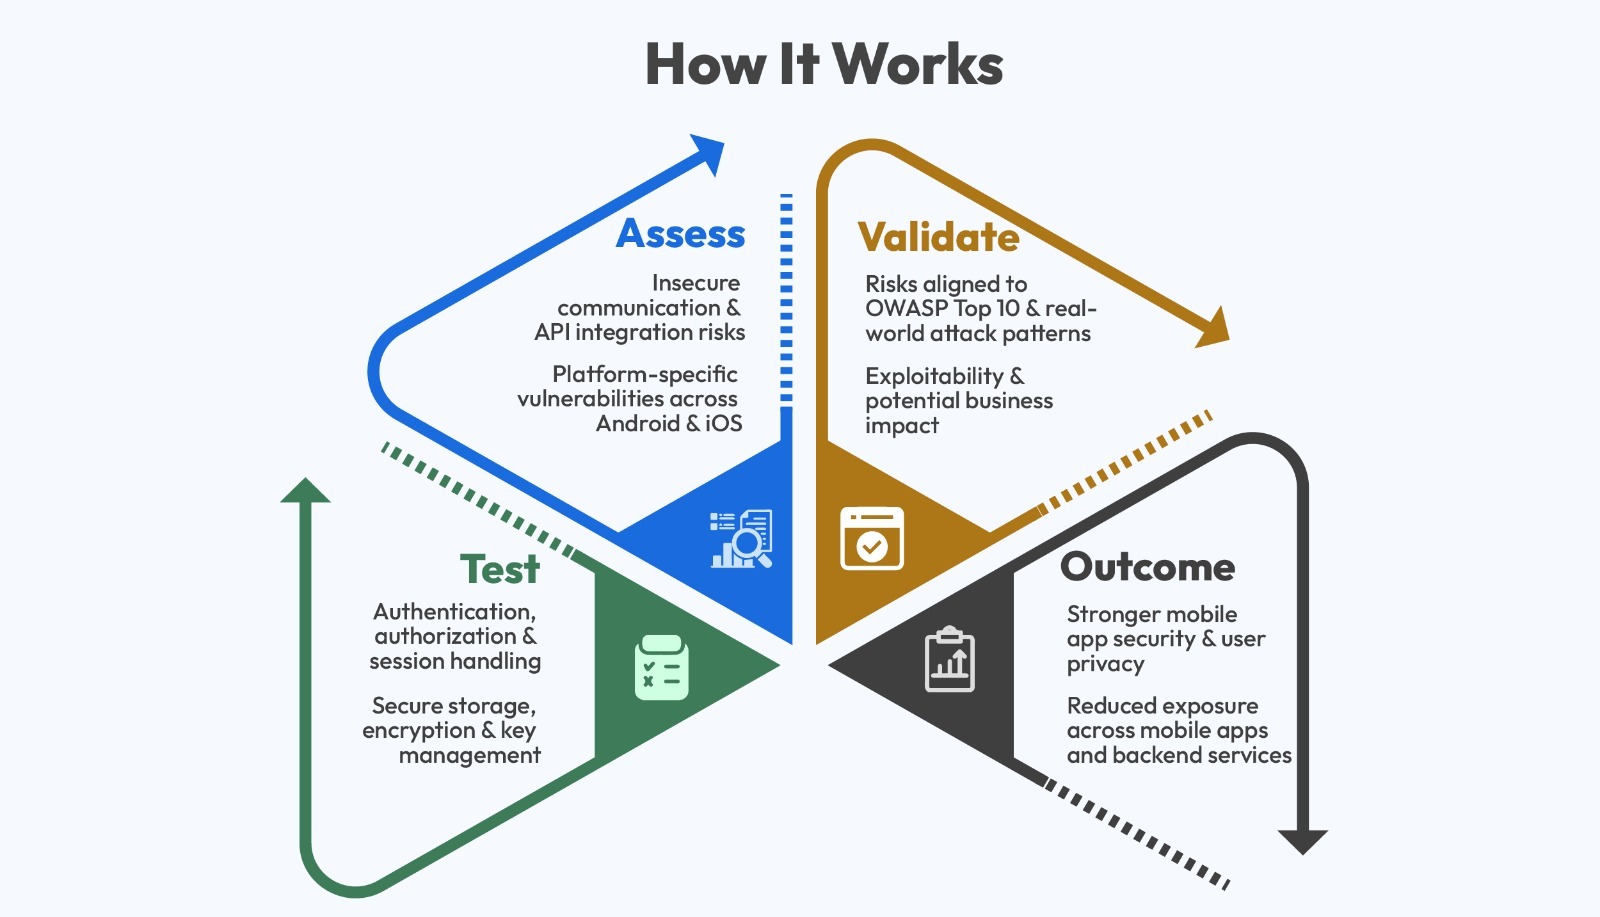
CyRAACS assesses Android and iOS applications for vulnerabilities that could expose sensitive data, compromise privacy, or enable unauthorized access, including how each app interacts with its backend.
⦁ Assess secure storage, encryption, and key management practices
⦁ Test authentication, authorization, and session handling
⦁ Assess risks aligned with OWASP Top 10 and real-world attack patterns
⦁ Identify insecure communication and API integration risks
⦁ Evaluate platform-specific vulnerabilities for Android and iOS
⦁ Deliver actionable recommendations to strengthen mobile application security
VAPT for RBI, SEBI, and PCI-DSS Compliance
Many Indian regulations require regular security testing. A VAPT audit, backed by a clear VAPT report, helps banks, NBFCs, and fintechs meet RBI and SEBI expectations and supports PCI-DSS, ISO 27001, and SOC 2 requirements. CyRAACS aligns every engagement with the evidence auditors request, so your assessment doubles as proof of compliance.
As one of the established VAPT and penetration testing companies in India, CyRAACS delivers vulnerability testing services and penetration testing services across India and the wider region.
Risk-driven, real-world testing that validates actual exploitability.
Aligned to OWASP, NIST, and industry best practices.
Practitioner-led assessments combining automated scans with manual pen testing.
Manual pen testing techniques across black-box, grey-box, and white-box approaches.
Clear, prioritized remediation guidance focused on business impact.
Consistent, deep coverage across applications, APIs, infrastructure, and cloud.
Frequently Asked Questions
Vulnerability Assessment and Penetration Testing (VAPT) is a combined security testing approach that first finds weaknesses, then validates whether an attacker could actually exploit them. In cybersecurity, VAPT gives you a real picture of risk instead of a list of theoretical issues.
Unlike basic scanning tools, our VAPT services combine automated scans with expert-led manual testing to validate real-world exploitability. This approach helps eliminate false positives, uncover business logic vulnerabilities, and provide risk-based, actionable remediation guidance.
CyRAACS provides comprehensive VAPT coverage across:
This ensures end-to-end security testing across your entire attack surface
Organizations should conduct VAPT regularly—especially:
Continuous or managed VAPT is recommended to address evolving threats and maintain a strong security posture.
CyRAACS provides:
This enables teams to act quickly and effectively to reduce security risks
Yes. CyRAACS supports organizations beyond the assessment by providing clear remediation guidance, helping teams understand the impact of vulnerabilities, and validating fixes once they are implemented. This ensures that identified risks are effectively addressed and not just documented.
CyRAACS conducts VAPT in a controlled and carefully planned manner to minimize any disruption to business operations. Testing is scheduled in coordination with your team, and exploit validation is performed responsibly to ensure systems remain stable and secure during the assessment.
In cybersecurity, VAPT means pairing a vulnerability assessment, which finds weaknesses, with penetration testing, which proves whether those weaknesses can be exploited. Together, they show both what is wrong and what an attacker could actually do with it.
A CyRAACS VAPT report includes detailed findings with risk ratings, proof of exploitability and business impact, and prioritized, step-by-step remediation guidance. It is written to be useful to both technical teams and auditors.
A VAPT audit is a structured assessment used to demonstrate security testing for regulatory or certification purposes, such as RBI, SEBI, PCI-DSS, ISO 27001, or SOC 2. The resulting report serves as evidence that testing was performed and findings were addressed.
Related Resources