






Red Team vs Blue Team: What’s the Difference?
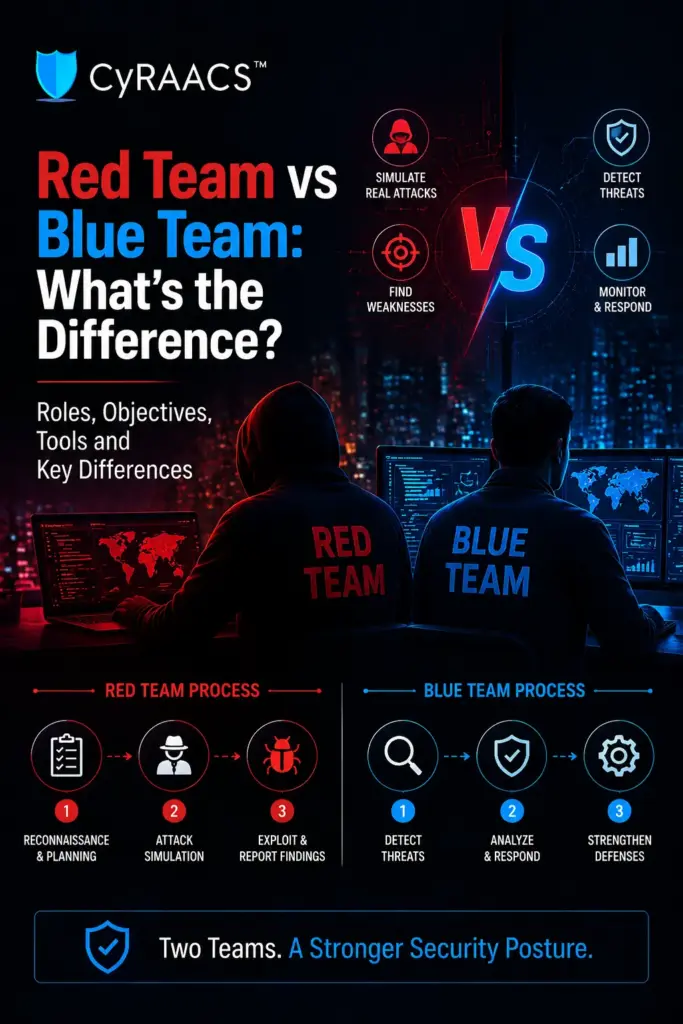
Cybersecurity needs both attack and defence. A red team simulates an attacker to test how an organisation could be compromised, while a blue team protects the environment, detects threats, and responds to attacks. NIST describes the red team as an authorised group that emulates adversary capabilities, while the blue team is responsible for maintaining the […]
CERT-In Empanelled Auditors List 2026: How to Find and Verify an Approved Auditor
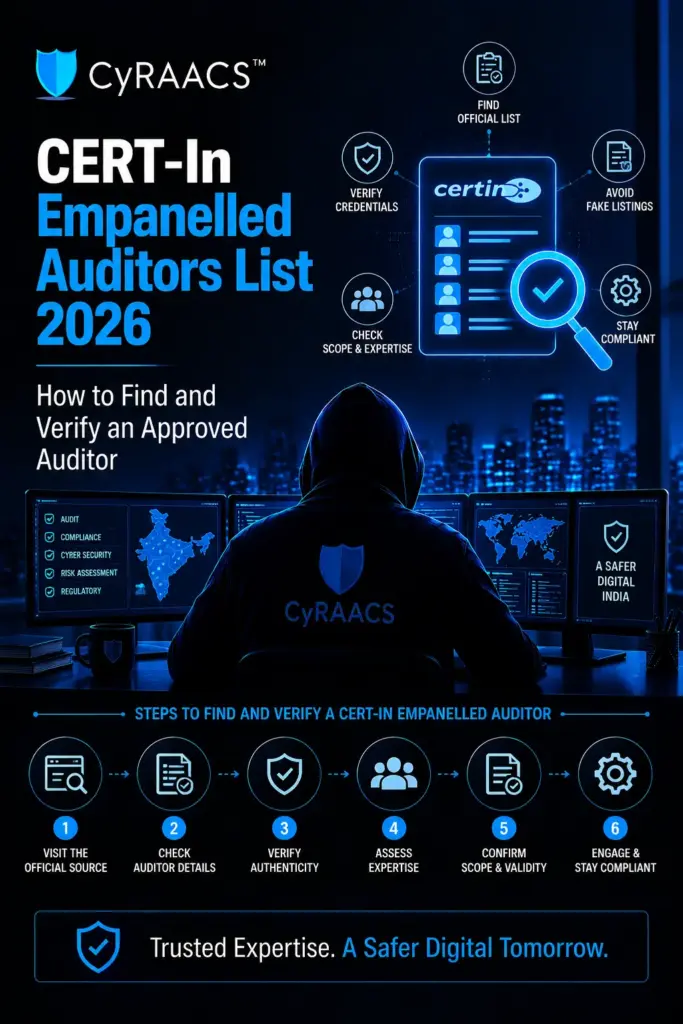
A vendor displaying a CERT-In badge on its website does not automatically prove that the firm is currently empanelled. Before appointing an auditor, organisations should verify the firm’s legal name, current listing, and approved audit capabilities directly against the official CERT-In list. CERT-In stands for the Indian Computer Emergency Response Team. It has been operational […]
Top 10 Compliance Management Tools for 2026
Many organisations still manage compliance using spreadsheets. These files often have multiple tabs, several owners, and outdated versions shared across teams. During audits, finding the right information becomes time-consuming, and important details can easily be missed. Today, this approach is no longer enough. Compliance requirements have grown with regulations such as DPDPA, RBI guidelines, SOC […]
What Is ISO Compliance? Requirements, Benefits, and Certification Process Explained
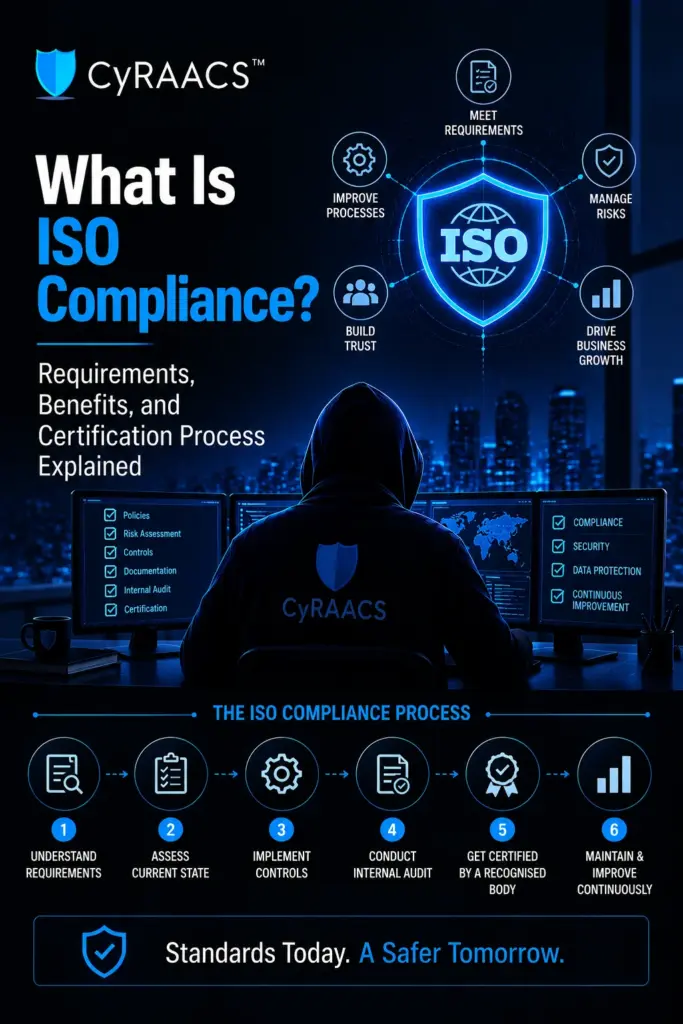
ISO compliance and ISO certification are often used interchangeably. They do not. Understanding the difference is important when customers, regulators, or procurement teams ask your organisation to demonstrate compliance or provide an ISO certificate. For information security, ISO/IEC 27001:2022 is one of the most widely used standards. It provides requirements for establishing, implementing, maintaining, and […]
What Is Security Testing? Types, Methods, Tools and Best Practices
Security testing helps organisations identify weaknesses in applications, systems, and networks before attackers can exploit them. It is an important part of a wider cybersecurity programme, especially as applications become more complex and organisations rely on APIs, cloud services, open-source software, and AI. The financial impact of missing these weaknesses can be significant. IBM’s 2026 […]
A 101 Guide to Web Application Security
A healthcare provider once had a SQL injection vulnerability sitting in an overlooked part of its application for months. When attackers eventually exploited it, the incident exposed the protected health information of millions of patients. The vulnerability itself was not new or technically complex. The problem was that an existing weakness remained unnoticed for too […]
What Is Threat Modelling? Steps, Frameworks and Examples
of waiting to find vulnerabilities after development or deployment, teams assess how a system could be attacked and decide how to address those risks. It is not a one-time document or a security tool. It is a structured process that examines the system, identifies potential threats, prioritises risks, and validates the controls in place. This […]
Web Application Penetration Testing: Process and Checklist
A web application penetration test checks whether an attacker can exploit security weaknesses in a real application. It goes beyond automated scanning by testing authentication, access controls, APIs, business logic, and other areas that may expose data or functionality. A vulnerability scanner can identify potential weaknesses, but a penetration test goes further by validating whether […]
What Is SaaS Security? Risks, Best Practices and Checklist
SaaS applications are now part of almost every organisation’s daily operations, but managing their security is becoming harder as the number of apps, users, integrations, and data connections grows. The Cloud Security Alliance’s 2025 State of SaaS Security report found that 63% of organisations reported external data oversharing, while 58% struggled to enforce proper privileges […]
What Is Red Teaming? Process, Benefits and Examples
Red teaming is a controlled cybersecurity exercise that simulates how a real attacker could target an organisation. Instead of simply looking for vulnerabilities, a red team tries to achieve a defined objective while testing whether the organisation can detect and respond to the attack. In simple terms, a vulnerability assessment asks what is vulnerable, while […]