






VAPT Audits in 2026: Types, Process, and Why They Matter
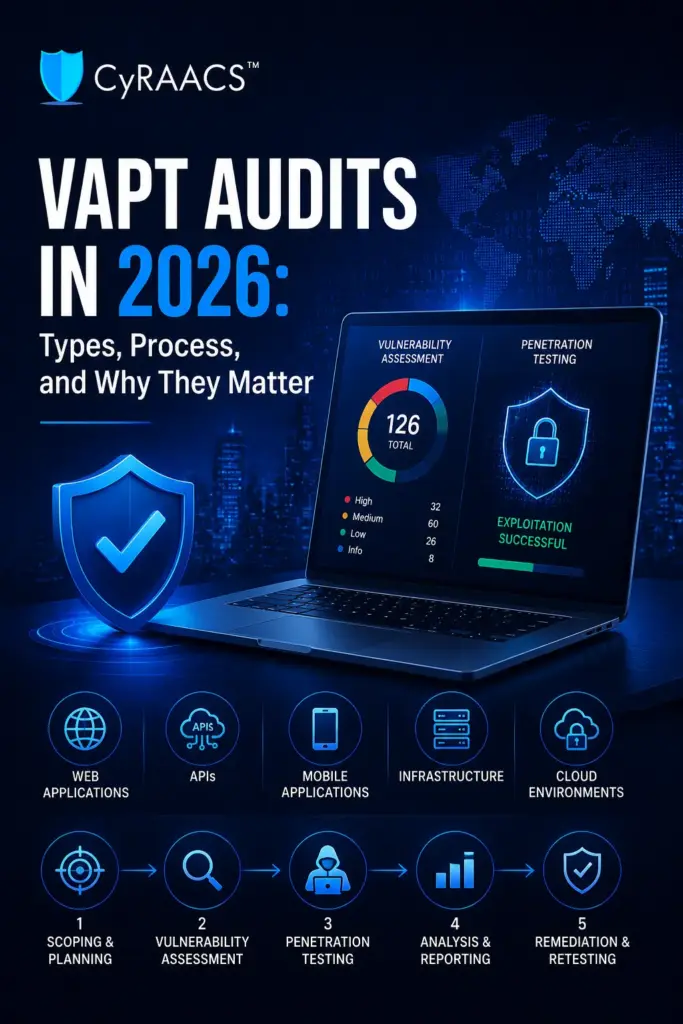
A security vulnerability is only a risk until someone can exploit it. The challenge for organisations is knowing which weaknesses are genuinely dangerous before an attacker finds them first. This is where Vulnerability Assessment and Penetration Testing (VAPT) becomes important. A well-planned VAPT engagement helps organisations identify vulnerabilities, test whether they can actually be exploited, […]
Security vs Compliance: Are They the Same Thing?
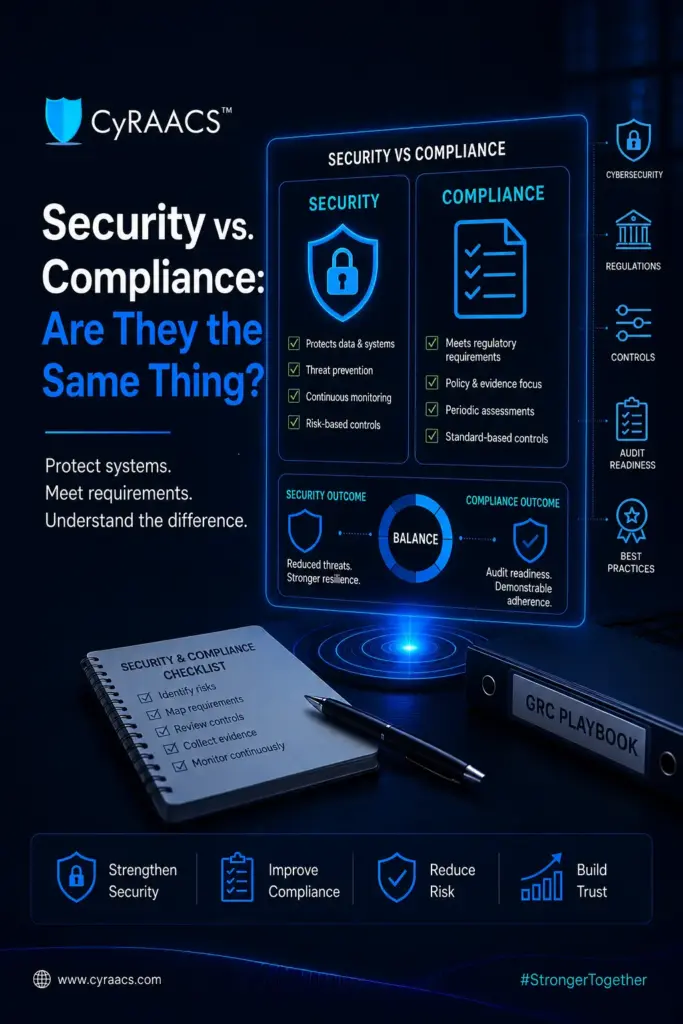
A company can be compliant and still get breached. It can also have strong security controls and still fail a compliance audit. This is because security and compliance solve different problems, even though they often use many of the same controls. Security focuses on protecting systems, data, and people from real-world threats. Compliance focuses on […]
Risk Appetite vs. Risk Tolerance: What’s the Real Difference?
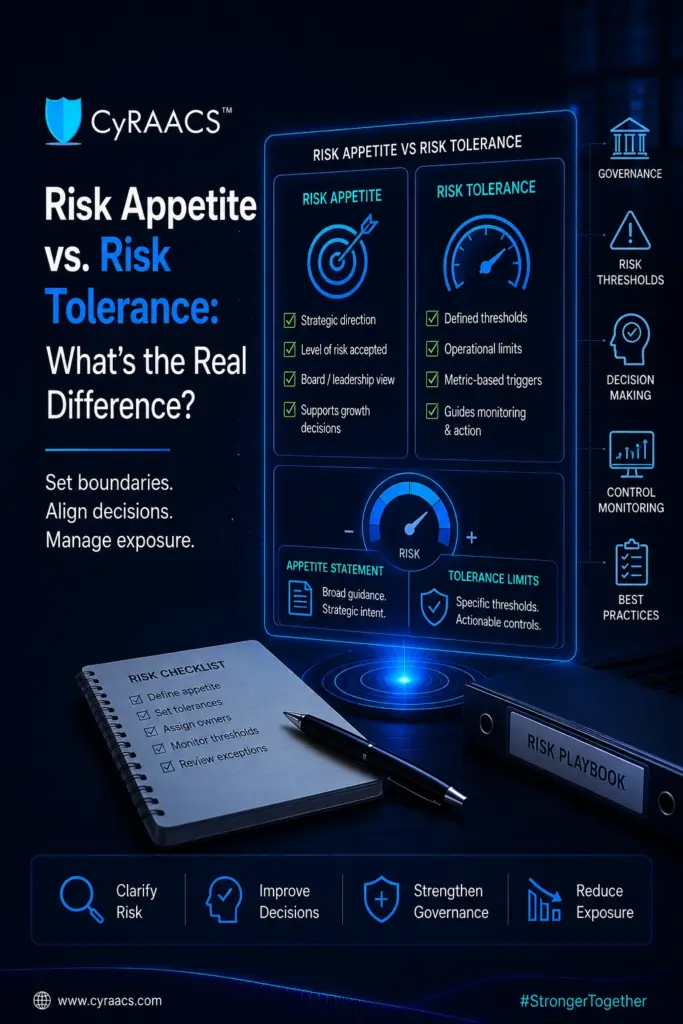
Every organisation talks about managing risk, but not every organisation speaks the same language. One of the most common areas of confusion is the difference between risk appetite and risk tolerance. Although these terms are often used interchangeably, they represent two distinct concepts that shape how an organisation makes decisions, allocates resources, and manages uncertainty. […]
How to Choose a Third-Party Risk Management Framework in 2026
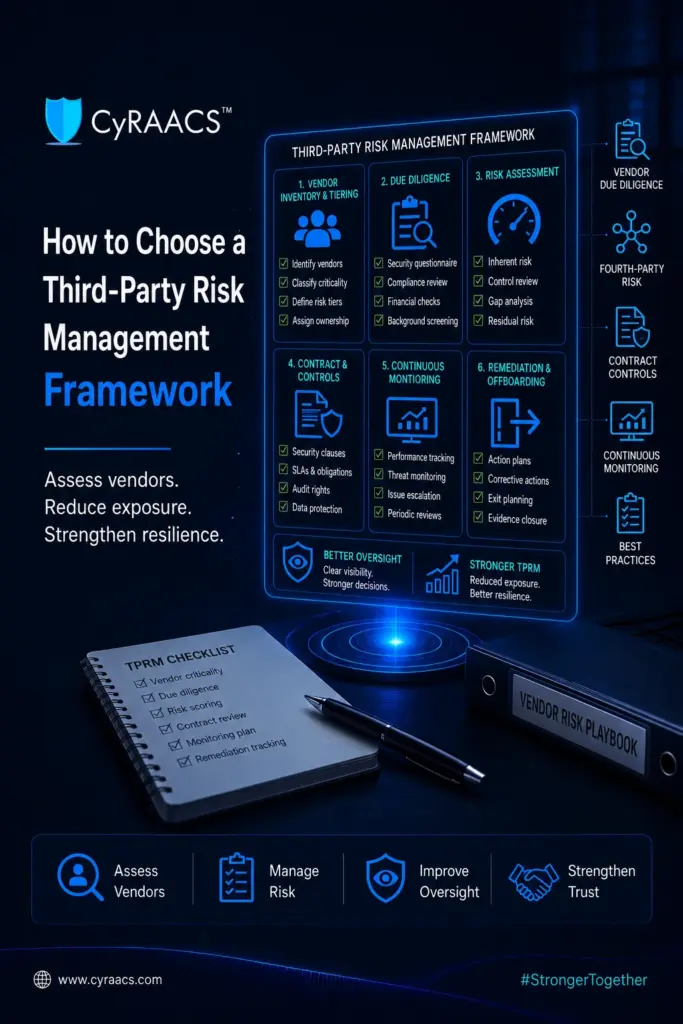
Your biggest cybersecurity risk may not be inside your organisation. It could be one of your vendors. According to IBM’s Cost of a Data Breach Report, the global average cost of a data breach has reached a record high, increasing by 12% over the previous year, driven by higher detection, escalation, and lost business. As […]
What Is the COSO Framework? A Practical Guide for IT and Security Leaders
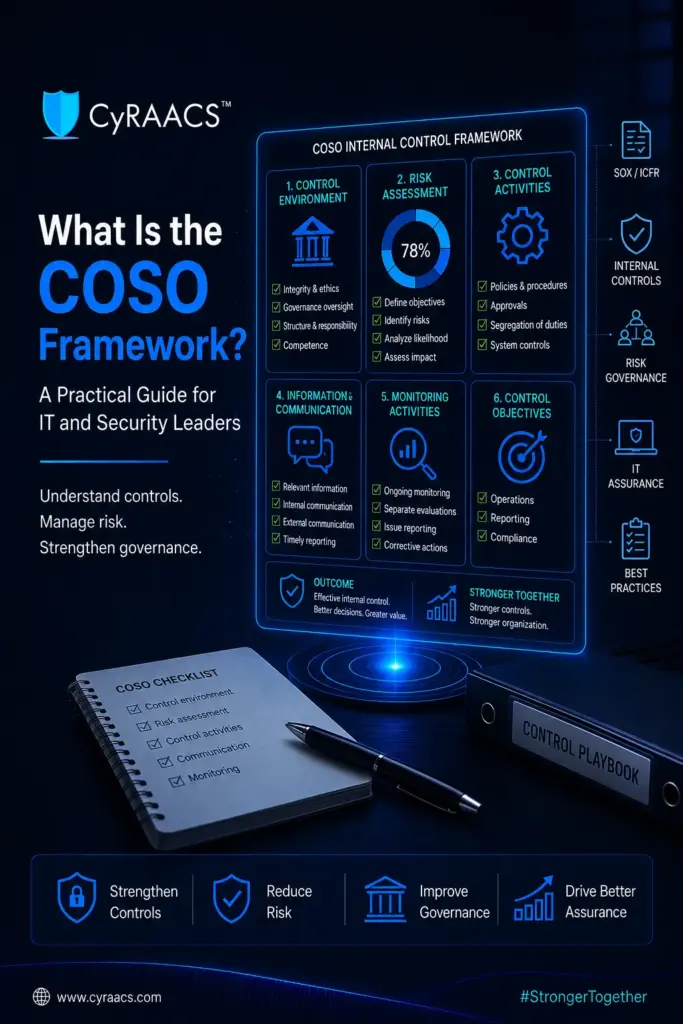
The auditors arrive, the policies are in place, and the CISO feels prepared. Then comes a simple question: How do you know your access controls worked over the last 12 months? Suddenly, everyone is searching for screenshots, emails, and reports. What should take minutes turns into weeks of chasing evidence. This isn’t because the controls […]
Understanding the DPDP Act Rules: What India’s New Data Privacy Rules Mean for Your Organisation
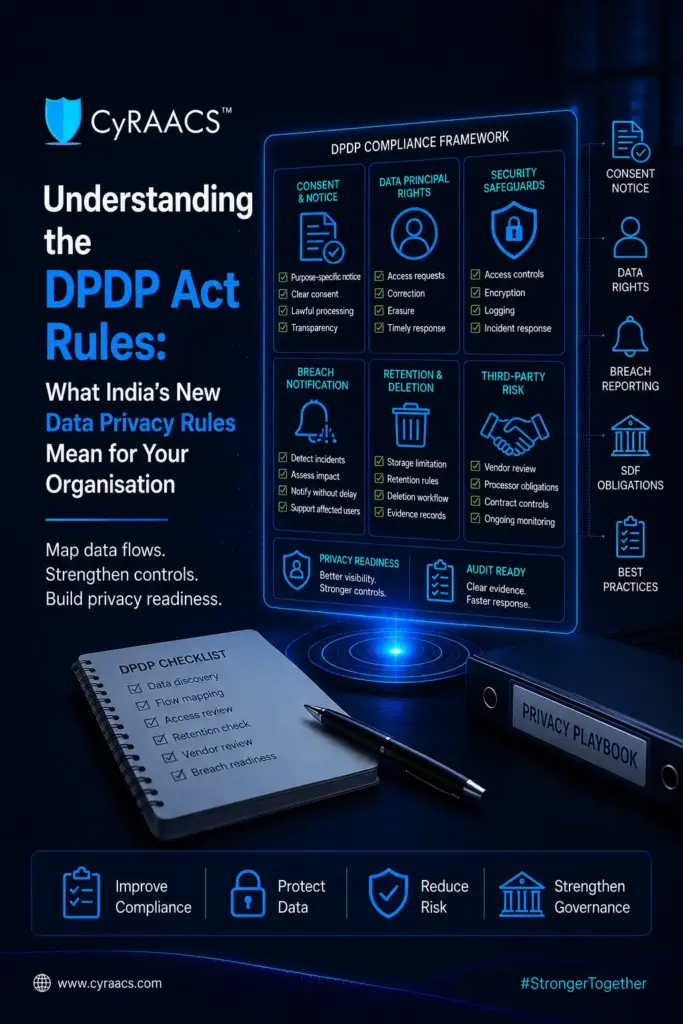
Ask a leadership team how their DPDPA preparation is going, and you will usually hear a confident answer. The privacy notice has been rewritten. Legal has reviewed the vendor contracts. Consent language has been drafted, redrafted, and approved. The policy binder is thick, current, and impressive. Now ask a different question. A customer filled in […]
All You Need to Know About Risk Management Frameworks
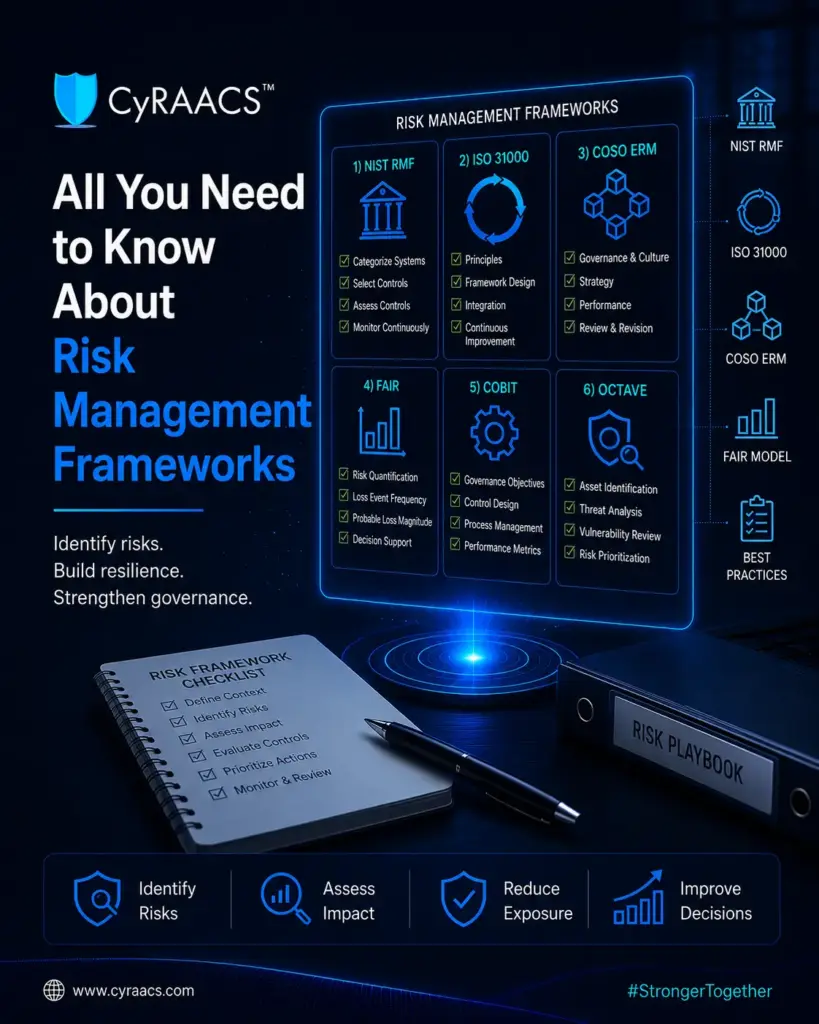
Every organisation manages risk. The question is whether it manages risk deliberately or accidentally. A finance team hedging currency exposure, an IT team patching a critical vulnerability at midnight, a procurement head quietly dropping an unreliable vendor: all of this is risk management. It is just risk management happening in fragments, with no shared language, […]
What is Compliance Testing, and How to Conduct It in 2026
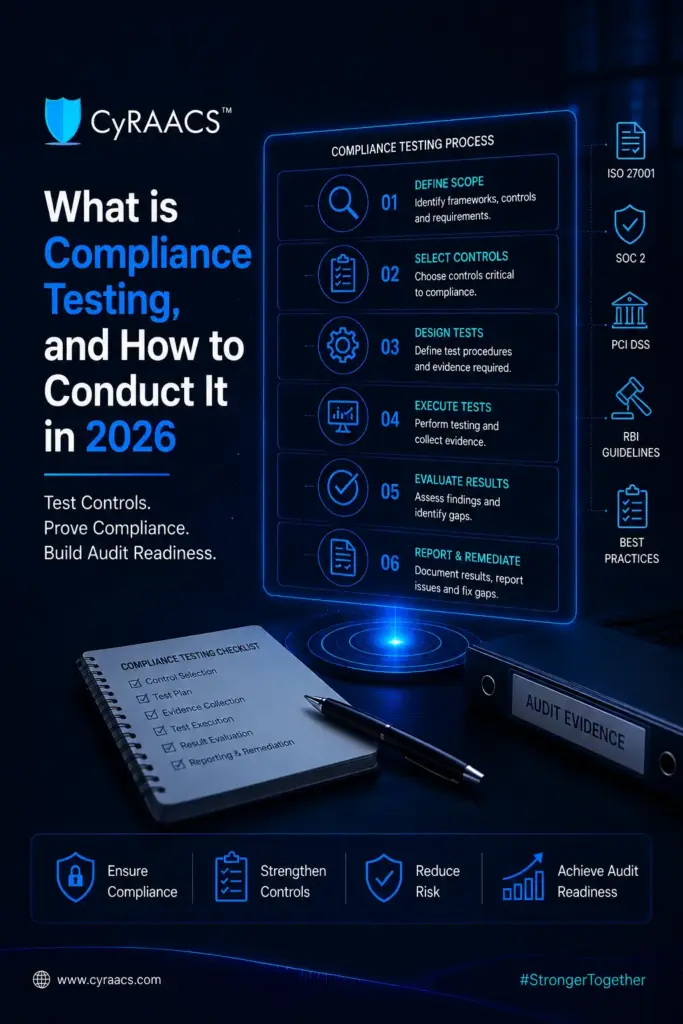
Your ISO 27001 audit is six weeks away, and the evidence folder looks complete. Every policy is signed, and every control is written down, but nothing has been tested. That gap is exactly what compliance testing closes, and skipping it is why teams get caught off guard mid-audit. CyRAACS sees this pattern before almost every […]
Top 10 GRC Tools & Platforms for Compliance Management in 2026
Every vendor on this list will call itself one of the right GRC tools for your compliance program, and this comparison discloses how the list was built and where each platform actually fits, without any vendor paying for placement. The top GRC tools for 2026: We compared these 10 named GRC platforms against three criteria: […]
Internal Control in Auditing: A Complete 2026 Guide
Your audit team keeps circling back to one question: are your internal controls strong enough to trust? That answer shapes how deeply the rest of your governance, risk, and compliance program gets tested this cycle. Internal control in auditing means the system of policies, procedures, and checks a company builds. It protects assets, keeps records […]