






Achieving ISO 27001 or SOC 2 certification is much more than documenting policies and implementing security controls. Organizations are increasingly expected to demonstrate that their security controls are effective through regular technical security assessments. One of the most common questions organizations ask is: “What security assessments are mandatory for ISO 27001 and SOC 2, and how often should they be performed?”
While neither ISO 27001 nor SOC 2 prescribes an exhaustive list of technical assessments, both frameworks require organizations to identify security risks, implement appropriate controls, and continuously validate their effectiveness. This is where Vulnerability Assessment and Penetration Testing (VAPT), API security testing, cloud configuration reviews, vulnerability management, and secure source code reviews become essential.
Understanding the Security Testing Expectations
ISO 27001 is a risk-based Information Security Management System (ISMS) standard that requires organizations to identify information security risks and implement controls that effectively mitigate those risks.
SOC 2, on the other hand, evaluates whether an organization’s controls are suitably designed and operating effectively to protect customer data based on the AICPA Trust Services Criteria, including Security, Availability, Processing Integrity, Confidentiality, and Privacy.
Although the two frameworks differ in structure, they share a common expectation: organizations must regularly validate the effectiveness of their security controls through technical assessments and continuous monitoring.
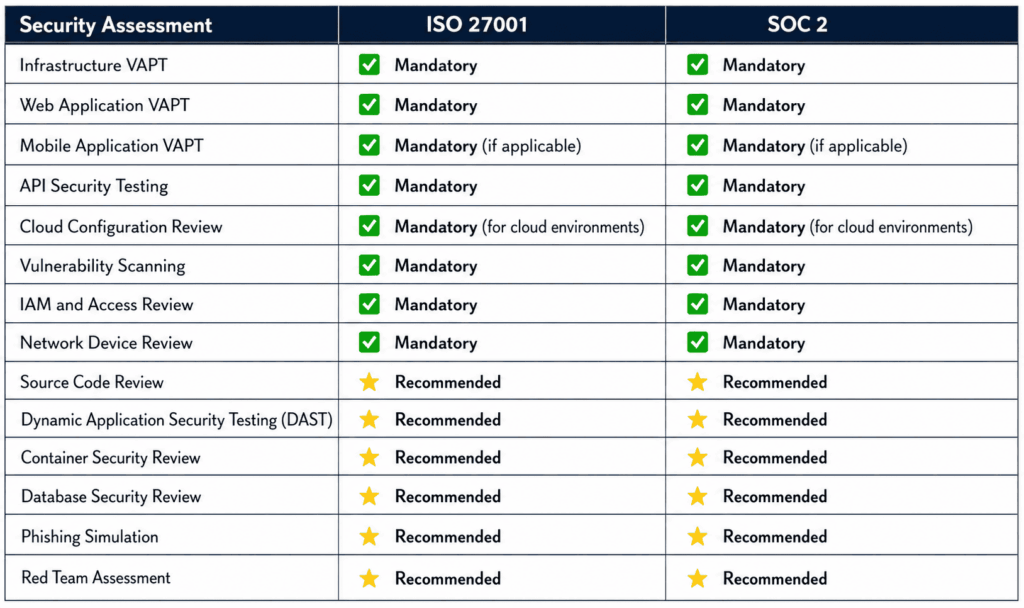
ISO 27001 vs SOC 2: Security Assessment Requirements briefly
The table below summarizes the key security assessments that organizations should perform to meet the expectations of both ISO 27001 and SOC 2 auditors.
What Does This Mean?
Organizations preparing for ISO 27001 or SOC 2 should prioritize the mandatory security assessments as part of their annual cybersecurity program. These assessments provide objective evidence that security controls are operating effectively and demonstrate compliance with auditor expectations.
The recommended assessments, while not explicitly mandated by either framework, significantly improve an organization’s security maturity. They are increasingly requested during enterprise customer due diligence, third party risk assessments, and supplier security reviews.
Best Practice: Rather than running separate programs for ISO 27001 and SOC 2, organizations should implement a unified security testing strategy that satisfies the requirements of both frameworks. This approach reduces audit effort, eliminates duplicate testing, lowers costs, and strengthens overall cybersecurity resilience.
After this section, continue with the remainder of your blog beginning with:
- Mandatory Security Assessments
- Infrastructure VAPT
- Web Application Penetration Testing
- API Security Testing
- Cloud Configuration Review
- Vulnerability Scanning
- Source Code Review
How CyRAACS Can Help
At CyRAACS, we help organizations build robust security assurance programs that align with ISO 27001, SOC 2, PCI DSS, RBI, SEBI, DPDPA, and other global regulatory requirements.
As a CERT-In Empaneled and CREST Accredited cybersecurity consulting organization, our team combines deep technical expertise with practical compliance knowledge to deliver security assessments that not only identify vulnerabilities but also help organizations strengthen their overall security posture.
Our security assessment services include:
- External and Internal Infrastructure VAPT
- Web Application Penetration Testing
- Mobile Application Penetration Testing
- API Security Testing
- Cloud Configuration Reviews for AWS, Azure, and Google Cloud
- Secure Source Code Reviews
- Network Device Security Reviews
- Container and Kubernetes Security Assessments
- Red Team Exercises
- Secure Configuration and Hardening Reviews
- Continuous Vulnerability Management
- Compliance Driven Security Testing for ISO 27001, SOC 2, PCI DSS, RBI, SEBI, HIPAA, and DPDPA
Our consultants hold globally recognized certifications including OSCP, OSWE, CRTO, CISSP, CISA, ISO 27001 Lead Auditor, AWS Security, Azure Security, and cloud security certifications, enabling us to deliver assessments that meet the expectations of customers, regulators, and certification bodies. Beyond identifying vulnerabilities, CyRAACS provides detailed remediation guidance, executive reporting, risk prioritization, and retesting support to help organizations close findings efficiently and demonstrate continuous compliance. Whether you are preparing for your first ISO 27001 certification, undergoing a SOC 2 Type II audit, or strengthening your cybersecurity posture, CyRAACS can serve as your trusted security partner throughout your compliance journey.


