



Your complete beginner’s guide to understanding how CMaaS transforms compliance from a burden into a strategic advantage for modern organizations
The Compliance Puzzle: Why Traditional Approaches Fall Short
Think of compliance management like maintaining a complex machine. Every component needs regular attention, accurate documentation, and timely maintenance to keep the entire system working properly. Traditional compliance approaches often rely on disconnected spreadsheets, manual reporting, and separate teams handling different regulatory requirements.
This creates gaps in communication, inconsistent processes, and delays in identifying compliance risks. As regulations evolve and businesses expand into new markets, managing everything internally can become increasingly difficult. The challenge is not simply understanding the rules. It is building a consistent system that helps the organization follow them every day.
What Exactly Is CMaaS?
Compliance Management as a Service (CMaaS) is an outsourced compliance solution that helps organizations manage regulatory requirements, internal policies, risk assessments, and compliance activities through specialized expertise and technology.
Unlike a traditional compliance management system, which refers to the internal tools, processes, and controls an organization uses to meet its obligations, CMaaS provides access to an external service provider that supports these activities.
A compliance management system may include risk assessments, policy management, employee training, internal controls, audits, and continuous monitoring. CMaaS brings many of these functions together through a managed service model, helping businesses maintain their compliance activities without having to build every capability internally.
CMaaS combines world-class specialists, automated platforms, and proven frameworks to keep your organization compliant across standards like RBI, SEBI, ISO 27001, GDPR, SOC 2, and more, without disrupting your core business.
The CMaaS Advantage: Why Smart Organizations Are Making the Switch
- Instant Expertise
Access to certified compliance professionals who specialize in your industry’s specific requirements – no hiring headaches or training delays.
- Cost Efficiency
Reduce compliance costs by up to 30% compared to building internal teams. Pay for expertise only when you need it.
- Automated Monitoring
Continuous compliance monitoring and reporting with proactive, real-time compliance oversight and issue alerts, catching issues before they become costly problems.
- Scalable Solutions
Grow or shrink your compliance needs instantly without the overhead of permanent staff or infrastructure investments.
Core Components: What’s Under the CMaaS Hood
- Risk Assessment & Gap Analysis
Comprehensive evaluation of your current compliance posture, identifying vulnerabilities and improvement opportunities across all regulatory frameworks.
- Policy Development & Management
Creation and maintenance of tailored policies, procedures, and controls that align with industry standards and regulatory requirements.
- Continuous Monitoring & Reporting
An effective compliance program also needs clear responsibilities and oversight. The board of directors and senior management help establish a culture of compliance by setting expectations, approving policies, and reviewing significant compliance risks.
A dedicated compliance officer or compliance manager can coordinate the day-to-day compliance function. Responsibilities may include maintaining policies, tracking regulatory changes, reviewing emerging risks, coordinating employee training, communicating audit findings, and following up on corrective actions.
Employees and business teams also play an important role. Clear reporting structures, assigned responsibilities, and documented workflows help ensure that compliance requirements are followed consistently across departments.
Compliance Frameworks: Your CMaaS Covers All the Bases
Real-time compliance tracking with automated alerts, detailed reporting, and executive dashboards for complete visibility.
| SOC 2 Service organization controls for security, availability, and processing integrity | ISO 27001 International standard for information security management systems |
| GDPR European data protection and privacy regulation compliance | HIPAA Healthcare information privacy and security requirements |
CyRAACS covers frameworks beyond those listed above: ISO 27001, NIST 800-53, RBI, IRDAI, SEBI, UIDAI, NESA, SAMA, PDPL, CSA STAR, and other global standards. Think of CMaaS as your compliance Swiss Army knife – one solution that adapts to handle dozens of different regulatory requirements. Whether you’re dealing with PCI DSS for payment processing or NIST frameworks for federal contractors, CMaaS providers maintain expertise across the entire compliance landscape.
The ROI Reality: What CMaaS Actually Costs vs. Saves
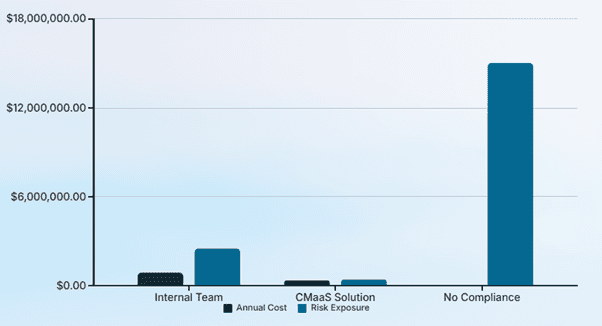
The numbers tell a compelling story. Organizations typically see 30% cost reduction, increased audit readiness, and lower consulting costs, within the first year of CMaaS implementation, with many reporting even higher returns as they avoid costly compliance failures and data breaches.
Getting Started: Your CMaaS Implementation Roadmap
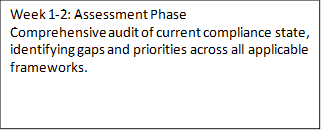
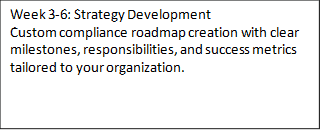
- The journey begins with a thorough compliance health check, where CyRAACS specialists engage your leadership and operational teams to map every regulation relevant to your sector. This isn’t a one-size-fits-all scan, it’s a tailored blueprint created to spotlight your true priorities and potential blind spots.
- Once the landscape is clear, CyRAACS walks your team through standards selection, helping you focus on regulations that not only keep you legal but also make you resilient and trusted in your market.
- Onboarding is designed to empower, not overwhelm. Interactive workshops, simple platform walkthroughs, and role-based assignments ensure that every team member knows what to do, when, and why. CyRAACS treats onboarding as an investment in your confidence and capability.
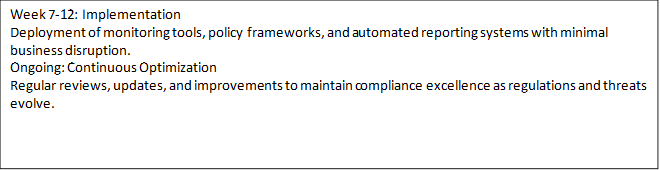
- Implementation is collaborative: individual compliance responsibilities are clearly mapped to business functions, making it easier to spot gaps and celebrate successes. Automated task lists guide users through daily and monthly actions, turning compliance from a worry into a routine.
- Continuous monitoring features in the platform deliver timely alerts and visual dashboards, helping your team track real progress and prepare for reviews with confidence.
- Regular review meetings with CyRAACS advisors ensure your compliance program not only keeps pace with new regulations, but also evolves as your business grows – so you’re always ready for change, never caught off guard.
Your Next Step: Transform Compliance from Cost Centre to Competitive Advantage
Compliance doesn’t have to be the organizational equivalent of paying taxes, necessary but painful. With CMaaS, it becomes a strategic differentiator that builds customer trust, reduces risk, and frees your team to focus on core business objectives.
How Does CyRAACS’ CMaaS Work?
Compliance as a Service is designed for growth and resilience. Its architecture lets customers instantly add new standards, map new regulatory requirements, or adapt existing procedures for expansion into new markets. Policy updates, incident tracking, and evidence-gathering are integrated into each workflow, creating a living compliance program that meets today’s needs and tomorrow’s changes.
CyRAACS backs this platform with a credentialed team and a proven track record across industries—delivering proactive support, real-world expertise, and trustworthy guidance however your business evolves.
- Unified Compliance Platform: CyRAACS’ Compliance as a Service, supports unified, mapped controls with customizable frameworks, with audit-ready records and all standards in one portal
- Pre-Built Workflows: CyRAACS’ Compliance as a Service maps regulatory requirements to repeatable tasks. As new laws arrive, the system updates itself, so your compliance never lags behind.
- Dedicated Support: Compliance isn’t just about ticking checklists. The CyRAACS team becomes your extended compliance department, guiding you through risk assessments, internal audits, policy updates, and continuous improvement.
Compliance Audits and Assessments
Compliance audits help organizations evaluate whether their policies, controls, and business activities meet applicable regulatory requirements. Internal reviews can identify weaknesses before they become larger problems, while independent external audits can provide an additional assessment of compliance practices.
A structured CMaaS approach can help businesses organize compliance documentation, maintain audit-ready evidence, track findings, and coordinate corrective actions. This makes it easier to demonstrate accountability during regulatory reviews.
Continuous Compliance Monitoring
Compliance is not a one-time activity. Regulations, business operations, and security risks can change throughout the year. Continuous monitoring helps organizations identify potential gaps, review control performance, and respond to emerging compliance issues.
Monitoring activities may include reviewing policies, checking control implementation, tracking outstanding tasks, assessing employee training, and following up on corrective actions. Automated alerts and dashboards can help compliance teams identify issues and maintain visibility across different business functions.
Compliance Accountability and Corrective Actions
An effective compliance program requires clearly defined ownership. Each department and responsible employee should understand the controls they manage, the tasks they need to complete, and the process for reporting potential issues.
When a compliance gap is identified, organizations should document the issue, assign responsibility, establish a corrective action plan, and monitor progress until the matter is resolved. This process supports accountability and continuous improvement.
Who Needs Compliance Management as a Service?
CMaaS can be useful for organizations that operate in regulated industries, manage sensitive information, or need to demonstrate compliance with multiple regulatory frameworks.
- Financial Institutions: Banks, financial service providers, and fintech companies may need support managing regulatory requirements, internal controls, and compliance reporting.
- Healthcare Organizations: Healthcare providers and related businesses handling sensitive patient information may need structured privacy, security, and compliance processes.
- Technology and SaaS Companies: Businesses that process customer data or provide cloud-based services may need help managing information security standards, customer requirements, and data protection obligations.
- Growing Businesses: Companies expanding into new markets may face additional regulatory requirements and benefit from access to external compliance expertise.
- Organizations Preparing for Audits: Businesses seeking certifications or preparing for regulatory assessments may use CMaaS to organize documentation, identify gaps, and track remediation activities.
The exact services required depend on an organization’s industry, size, business activities, and applicable regulatory obligations.
Frequently Asked Questions About CMaaS
1. What is Compliance Management as a Service (CMaaS)?
CMaaS is a managed compliance service that helps organizations handle regulatory requirements, risk assessments, policies, monitoring, and compliance reporting through external specialists and technology.
2. What is the difference between CMaaS and a compliance management system?
A compliance management system is the collection of internal processes, policies, tools, and controls used to meet regulatory requirements. CMaaS is a managed service model that provides external expertise and support for these compliance activities.
3. Why is compliance monitoring important?
Continuous compliance monitoring helps organizations identify potential gaps, track regulatory responsibilities, and address issues before they develop into larger compliance problems.
4. Which businesses can benefit from CMaaS?
Financial institutions, healthcare organizations, technology companies, SaaS providers, and growing businesses with complex regulatory requirements may benefit from CMaaS.
5. Does CMaaS replace an organization’s internal compliance team?
Not necessarily. CMaaS can support or extend an internal compliance team by providing specialized expertise, technology, monitoring, and reporting. The organization remains responsible for its regulatory obligations and oversight.
More to Explore
CyRAACS Compliance Management Services
Ready to Get Started?
Contact CyRAACS today for a free compliance assessment and discover how CMaaS can transform your organization’s approach to regulatory requirements.
Remember: In today’s regulatory landscape, compliance isn’t optional – but struggling with it alone is. Let the experts handle what they do best, so you can focus on what you do best.
Curious how it works for your business?
Book a free compliance assessment with CyRAACS expert and experience CMaaS advantage first-hand